Sponsored by AI-RMF® LLC

Home
Security of AI
Governance
Security
Assurance
Risk Navigator
ATLAS Navigator
Vulnerability Navigator
Assurance Navigator
Test
Threats
Videos
About
Home
Security of AI
Governance
Security
Assurance
Risk Navigator
ATLAS Navigator
Vulnerability Navigator
Assurance Navigator
Test
Threats
Videos
About
More
  • Home
  • Security of AI
  • Governance
  • Security
  • Assurance
  • Risk Navigator
  • ATLAS Navigator
  • Vulnerability Navigator
  • Assurance Navigator
  • Test
  • Threats
  • Videos
  • About
  • Home
  • Security of AI
  • Governance
  • Security
  • Assurance
  • Risk Navigator
  • ATLAS Navigator
  • Vulnerability Navigator
  • Assurance Navigator
  • Test
  • Threats
  • Videos
  • About

Security of AI™ is the Resource for Responsible AI (RAI)

Security of AI™ provides practical guidance, interactive tools, risk frameworks, technical resources, videos, books, and analysis covering topics such as the NIST AI Risk Management Framework, MITRE ATLAS, OWASP guidance, AI Red Teaming, Adversarial AI, AI System Security, Governance, Testing, Validation, and Assurance. 


Whether you're new to artificial intelligence or an expert responsible for deploying system, we have tools and tactics for you. Security of AI™ is designed to help you move from simply asking “Can we use AI?” to answering the more important question: “Can we Trust this AI system?”

Site Map: Quick Reference

For Navigation Ease, You can select a button below or browse
What is Security of AI™ >>>SOAI Governance Method >>>SOAI Security Method >>>SOAI Assurance Method >>>AI Risk Intelligence Navigator >>>MITRE ATLAS™ Intelligence Navigator >>>AI Vulnerability NavigatorAI Assurance Intelligence NavigatorRed Team Test Methods with Python Code >>>AI Threat Landscape >>>SOAI YouTube Channel >>>Security of AI™ Books on Amazon® >>>Book Consultation Services via AI-RMF® LLC

Security of AI™ Framework Description:

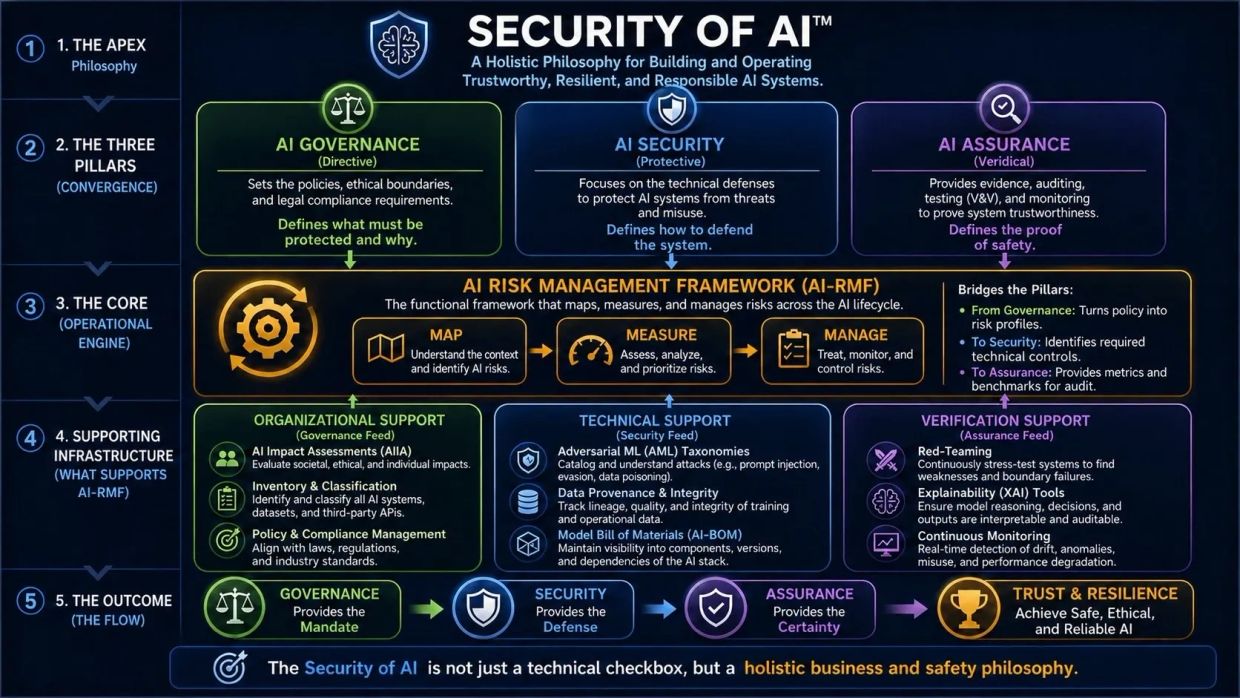
The Security of AI™ Framework is organized into five connected layers that move from philosophy to operational outcome. Together, these layers show how organizations can govern, secure, assess, and continuously improve AI systems throughout their lifecycle.

  1. The Apex — Philosophy
    The top layer establishes the overarching Security of AI™ philosophy: building and operating AI systems that are trustworthy, resilient, and responsible. It provides the strategic foundation for the entire framework.
  2. The Three Pillars — Convergence
    The second layer brings together the three core pillars:
    • AI Governance defines what must be protected and why.
    • AI Security defines how the system is defended.
    • AI Assurance provides the evidence needed to demonstrate that the system is operating as intended.
    • These pillars are designed to work together rather than as separate disciplines.

  1. The Core — Operational Engine
    At the center is the AI Risk Management Framework (AI-RMF), which serves as the operational engine of the model. Through the functions of Map, Measure, and Manage, organizations identify AI risks, assess and prioritize those risks, apply controls, and monitor risk across the AI lifecycle.
  2. Supporting Infrastructure — What Supports AI-RMF
    The fourth layer provides the organizational, technical, and verification capabilities needed to make AI risk management effective in practice. These include:
    • AI impact assessments
    • AI inventory and classification
    • Policy and compliance management
    • Adversarial machine learning threat analysis
    • Data provenance and integrity
    • AI Bills of Materials
    • Red-team testing
    • Explainability tools
    • Continuous monitoring
    • This layer provides the practical mechanisms that support governance, security, and assurance activities.

  1. The Outcome — The Flow
    The final layer shows how the framework produces its intended result. Governance provides the mandate, Security provides the defense, and Assurance provides the evidence and confidence. Together, these elements lead to the desired outcome: Trust and Resilience — safe, ethical, reliable, and defensible AI systems.

In this structure, Security of AI™ is not simply a cybersecurity model or compliance checklist. It is a five-layer operational philosophy that connects executive direction, governance, technical protection, assurance evidence, and risk management into a unified approach for trustworthy AI.
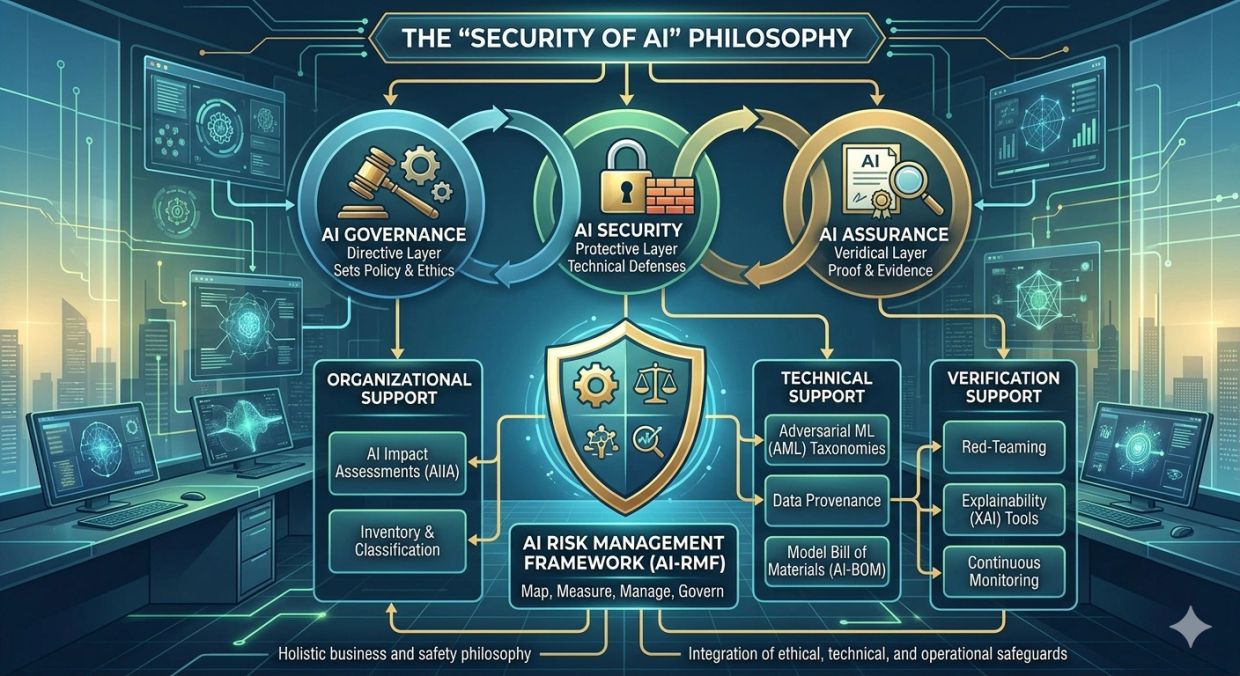
Diagram illustrating the 'Security of AI' philosophy with governance, security, assurance, and risk management framework.

Why is Security of AI™ Important?

Security of AI™ Philosophy

This is the overarching umbrella that integrates ethical, technical, and operational safeguards to ensure AI systems are trustworthy and resilient. 

The Three Pillars (Convergence)

  • AI Governance: The "Directive" layer. It sets the policies, ethical boundaries, and legal compliance requirements. It defines what must be protected and why.
  • AI Security: The "Protective" layer. It focuses on the technical defenses (e.g., adversarial hardening, data poisoning protection, and secure model weights). It defines how to defend the system.
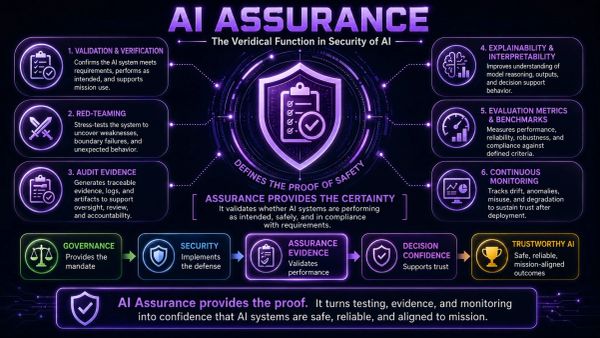
  • AI Assurance: The "Veridical" layer. It provides the evidence, auditing, and testing (V&V) to prove that the governance and security measures are working. It defines the proof of safety.

 The Operational Engine: AI-RMF

You use the Map, Measure, Manage, and Govern functions to bridge the pillars: 

  • Translate Governance policies into risk profiles. 
  • Identify technical Security controls based on those risks. 
  • Supply the metrics used for AI Assurance auditing. 

Supporting Infrastructure

You specialize in the sub-disciplines that feed the AI-RMF: 

  • Organizational: AI Impact Assessments (AIIA) and Inventory/Classification. 
  • Technical: Adversarial ML (AML) Taxonomies, Data Provenance, and AI-BOM (Bill of Materials). 
  • Verification: Red-Teaming, Explainability (XAI) Tools, and Continuous Monitoring. 

AI-RMF® LLC Consulting

Whether you're using, building, deploying, or acquiring artificial intelligence systems, AI-RMF® using our Security of AI™ Philosophy helps you operationalize AI-Governance.
Visit AI-RMF® LLC >>>

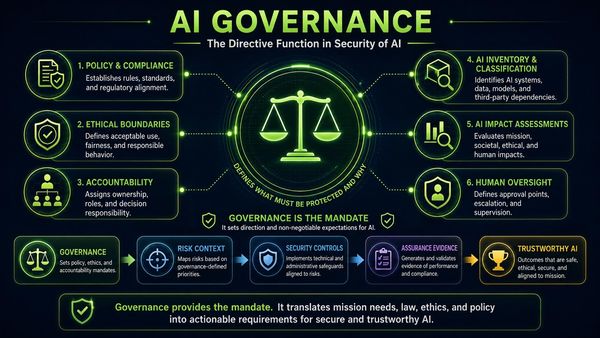
SOAI - Govern, Defend and Prove

1. Policy and Compliance

2. Ethical Boundaries

3. Accountability

4. Inventory and Classification

5. AI Impact Assessments

6. Human Oversight
Visit SOAI Governance >>>

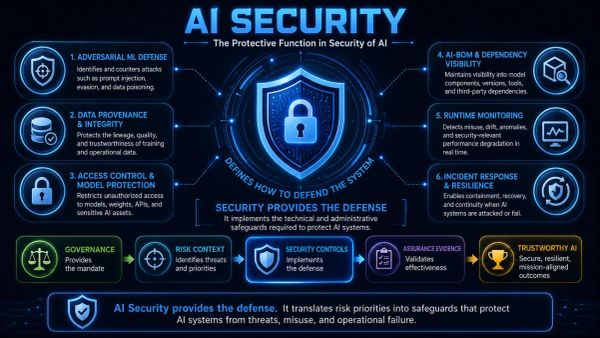
1. Adversarial ML Defense

2. Data Provenance and Integrity

3. Access Control and Model Protection

4. AI-BOM and Dependency Visibility

5. Runtime Monitoring

6. Incident Response and Resilience
Visit SOAI Security >>>

1. Validation and Verification

2. Red Team Testing

3. Audits with Evidence

4. Explainability and Interpretability

5. Evaluation Metrics and Benchmarks

6. Continuous Monitoring
Visit SOAI Assurance >>>

The interactive SOAI AI Risk Intelligence Navigator is awesome...Just click on a cell to explore the most critical AI risk:

1. Links 50 most critical AI Risk

2. Covers Five Risk Domains

3. Generates Likelihood and Impact Score

4. Generates a Risk Score

5. Provides Mitigation Guidance

6. Provides NIST, OWASP and MITRE ATLAS™ mapping

7. Free to use, No registration required.
Visit AI Risk Intelligence Navigator >>>

This interactive SOAI ATLAS™ Intelligence Navigator. Just click on a cell to understand  how adversaries attack systems:

1. Plain-English Descriptions

2. Provides Real World Scenarios

3. Generates a Severity Score

4. Provides Mitigation Guidance

5. Provides NIST and OWASP LLM Top-10 mapping

6. Free to use, No registration required.
Visit MITRE ATLAS™ Intelligence Navigator >>>

This interactive SOAI Vulnerability Intelligence Navigator.. Just click on a cell to understand how adversaries attack systems:

1. CVE/NVD correlation

2. Provide MITRE CWE software vulnerabilities

3. Correlates CISA KEV

4. Cross references NIST AI-100-2 Adversarial taxonomy

5. Cross References OWASP LLM Top-10 mapping

6. Free to use, No registration required.
Visit Vulnerabilty Intelligence Navigator >>>

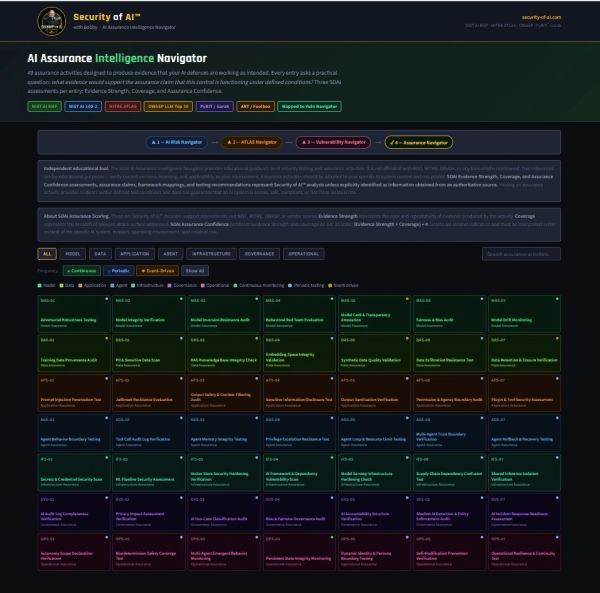
This interactive SOAI Assurance Intelligence Navigator.. Just click on a cell to understand what evidence demonstrates the defenses work.

1. What are we trying to demonstrate 

2. What testing or evaluation should be performed 

3. What evidence should be produced 

4. What artifact should document the results 

5. What vulnerabilities and attack techniques does the activity address.

6. Free to use, No registration required.
Visit AI Assurance Intelligence Navigator >>>

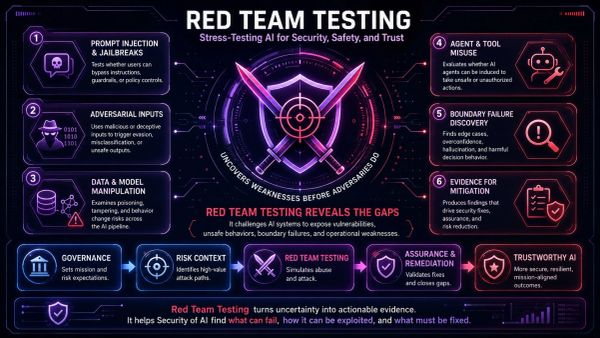
1. Prompt Injection and Jailbreaks

2. Adversarial Inputs

3. Data and Model Manipulation

4. Agent and Tool Misuse

5. Boundary Failure Discovery

6. Evidence for Mitigation
Visit SOAI Test >>>

Security Of AI™ Books on Amazon

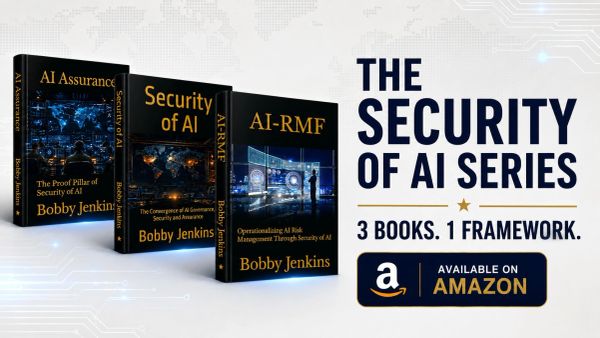
1. "Security of AI: The Convergence of AI Governance, Security and Assurance

2. "AI-RMF: Operationalizing AI Risk Management Through Security of AI"

3. "AI Assurance: The Proof Pillar of Security of AI"

Purchase our Books >>>

The goal of the "Security of AI" YouTube Channel is to raise awareness, provide educational opportunities and report of relevant SOAI News Commentary. We aim to help people, at all levels,  understand the impact and importance of AI-Governance, AI-Security and AI-Assurance.  We reveal life challenges and how AI systems fail in the real world—and what happens next. We produce AI security thrillers showing worst-case scenarios, breaking news analysis on live incidents and vulnerabilities, and deep-dive frameworks covering OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF. From Agentic AI threat modeling to Red Team Test techniques, we show defenders how to spot risks before they become disasters. 

Visit SOAI YouTube Channel >>>

Subscribe to Stay in Touch

"Your data and privacy is well respected". No data is shared with anyone!

Contact Us

Whether you're using, building, deploying, or acquiring artificial intelligence systems, AI-RMF® using our Security of AI™ Philosophy helps you operationalize AI governance, security and assurance.

Attach Files
Attachments (0)

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.

Reach Out for more information, project discussion request, or partnering opportunities.

AI-RMF® LLC

Bobby K. Jenkins Patuxent River, Md. 20670 Phone: 240-434-6889 -Text first with "SOAI-Your Name" to be verified. bobby@security-of-ai.com <<https://www.linkedin.com/in/bobby-jenkins-navair-492267239<<

Hours

Mon

By Appointment

Tue

By Appointment

Wed

By Appointment

Thu

By Appointment

Fri

By Appointment

Sat

Closed

Sun

Closed

AI-RMF® LLC

Copyright © 2026 Security-of-AI - All Rights Reserved.

Powered by

This website uses cookies.

We use cookies to analyze website traffic and optimize your website experience. By accepting our use of cookies, your data will be aggregated with all other user data.

Accept